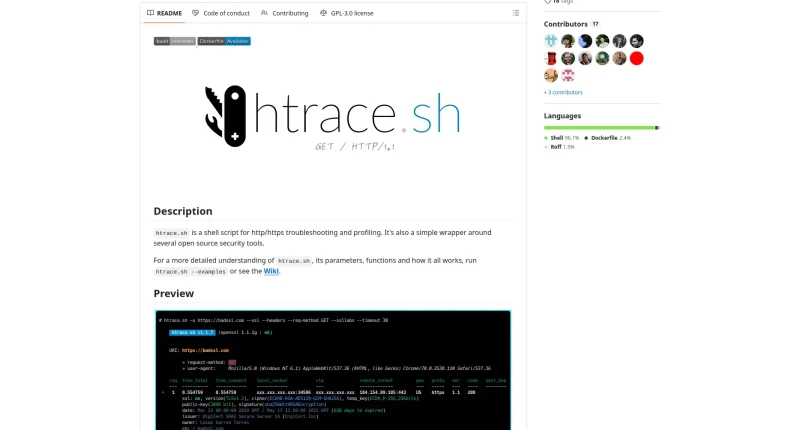
htrace.sh is a shell script for http/https troubleshooting and profiling. It's also a simple wrapper around several open source security tools.
htrace.sh is an open-source shell script designed for HTTP/HTTPS troubleshooting, profiling, and debugging. Created by trimstray, it functions as a Swiss Army knife that acts as a unified wrapper around several open-source security tools.
The main features of this tool include:
Standard HTTP/HTTPS Inspection: Allows developers and sysadmins to easily inspect target URLs (
-u), output basic SSL parameters (-s), view response headers (-h), and display response bodies (-b).Integrated Security Tools Wrapper: Bundles multiple external security scanners, including
testssl.sh(--testssl), Mozilla Observatory (--observatory), SSL Labs (--ssllabs),mixed-content-scan(--mixed-content), Nmap NSE (--nse), WAF detection viawafw00f(--waf), subdomain enumeration via Subfinder (--dns), and HTTP/2 testing vianghttp2(--http2).Request & Network Fine-Tuning: Supports custom HTTP request methods (
-M), custom request headers (-H), proxy servers (-p), host/port overrides (-r|--resolve), interface bindings (-i|--iface), and HTTP/TLS version specifications.Advanced Troubleshooting Controls: Includes flags for proxy cache bypassing (
--cache-bypass), SSL connection debugging (--ssl-debug), custom User-Agent/Referer headers, and hiding the source IP address in output logs (--hide-src-ip).Flexible Deployment Options: Can be installed natively via a setup script (
setup.sh) that places a symlink in/usr/local/binand a man page in/usr/local/man/man8, or built and executed as a standalone Docker container.Open-Source Shell Foundation: Written primarily in Shell script (96.1%) and released under the GPLv3 license.
You may also be interested in ...
Utopia
UIColors